The leader track 🤝 · for C-level, managers & DPOs · 6 x 45 min · no jargon
What the GDPR requires, when it reaches a non-EU company, and how each piece maps to the PDPA you already run - each session ends with questions to ask your DPO and legal counsel.
Why GDPR reaches a Singapore company
The Article 3 territorial-scope test - offer to or monitor people in the EU and you are in scope, no EU office required. And how that differs from the PDPA.
📜Leader 2 · easySeven principles, six lawful bases
The principles every processing must satisfy, and the six lawful bases - why consent is only one of them, unlike the PDPA's consent-first model.
🙋Leader 3 · mediumData-subject rights vs PDPA
Access, erasure, portability, objection and more - a broader set than the PDPA's access + correction. Which rights have no PDPA equivalent.
🔗Leader 4 · mediumController, processor, DPO, DPIA
Who is responsible for what, when a DPO is mandatory (narrower than the PDPA), and when a high-risk project needs an impact assessment.
🚨Leader 5 · decidingBreach (72h) + penalties
The 72-hour clock, the two-tier fines (up to 4% of global turnover), and the billion-euro cases - versus the PDPA's own regime.
🌐Leader 6 · decidingInternational transfers
Adequacy, Standard Contractual Clauses, and the post-Schrems II duty to assess the destination - the rules that govern moving EU data to Singapore.
The practitioner track 🛠️ · for DPOs, marketers & ops · 8 x 45 min · Lumina case
The operational half: how to comply in practice. Every session moves Lumina, a Singapore SaaS serving EU customers, one step closer to defensible GDPR compliance.
Does GDPR apply? the checker
A live Article 3 checker - answer three questions and see whether the GDPR reaches you, which article, and what to do next.
⚖️Practitioner 2 · easyPicking a lawful basis
Choose and document one of the six bases - consent vs legitimate interest, the consent standard, and the balancing test (LIA).
📄Practitioner 3 · mediumPrivacy notices + transparency
What Articles 13 and 14 require you to tell people, when, and how - the notice that turns "we process data" into informed consent.
🙋Practitioner 4 · mediumHandling a DSAR
A data-subject access request end to end - verify, locate, respond within one month, and the permitted extensions and refusals.
🗂️Practitioner 5 · hands-onRecords + DPIA
The Article 30 record of processing (and why the small-org exemption rarely helps), and when a project needs an impact assessment.
🌐Practitioner 6 · hands-onTransfers in practice
Put Standard Contractual Clauses in place and run a transfer impact assessment - the real work of moving EU data to a Singapore server.
🚨Practitioner 7 · hardestBreach response (72 hours)
The clock starts when you become aware. Assess the risk, notify the authority within 72 hours, and tell individuals when the risk is high.
🏛️Practitioner 8 · hardestThe GDPR program + PDPA harmony
Assemble the artifacts into one programme - and run GDPR and PDPA together so one operation satisfies both. Lumina graduates.
The running case + the live checker 🧭
Lumina, and a GDPR checker you can poke
The practitioner track follows Lumina, a fictional Singapore SaaS with EU customers - the exact situation where the GDPR reaches a company that has never set foot in Europe. Session b1 gives you a live checker: answer the three Article 3 questions and it tells you whether the GDPR applies and which limb catches you; a second mode suggests which of the six lawful bases fits a purpose. It encodes Articles 3 and 6 (educational, not legal advice).
Choose your path 🗺️
Two doors, one course. Leaders get the law and the risk; practitioners get the moves that make an EU-facing operation defensible.
The knowledge map 🧠
Both tracks at a glance - hover a session to spotlight its concepts, click any node to jump in.
The whole course on one sheet 📐
Seven modules: both tracks, the Article 3 test that decides whether the GDPR reaches you at all, the three lists everything else sits on, the practitioner ladder, who carries the legal duty, where Singapore teams get caught, and the 72-hour breach clock.
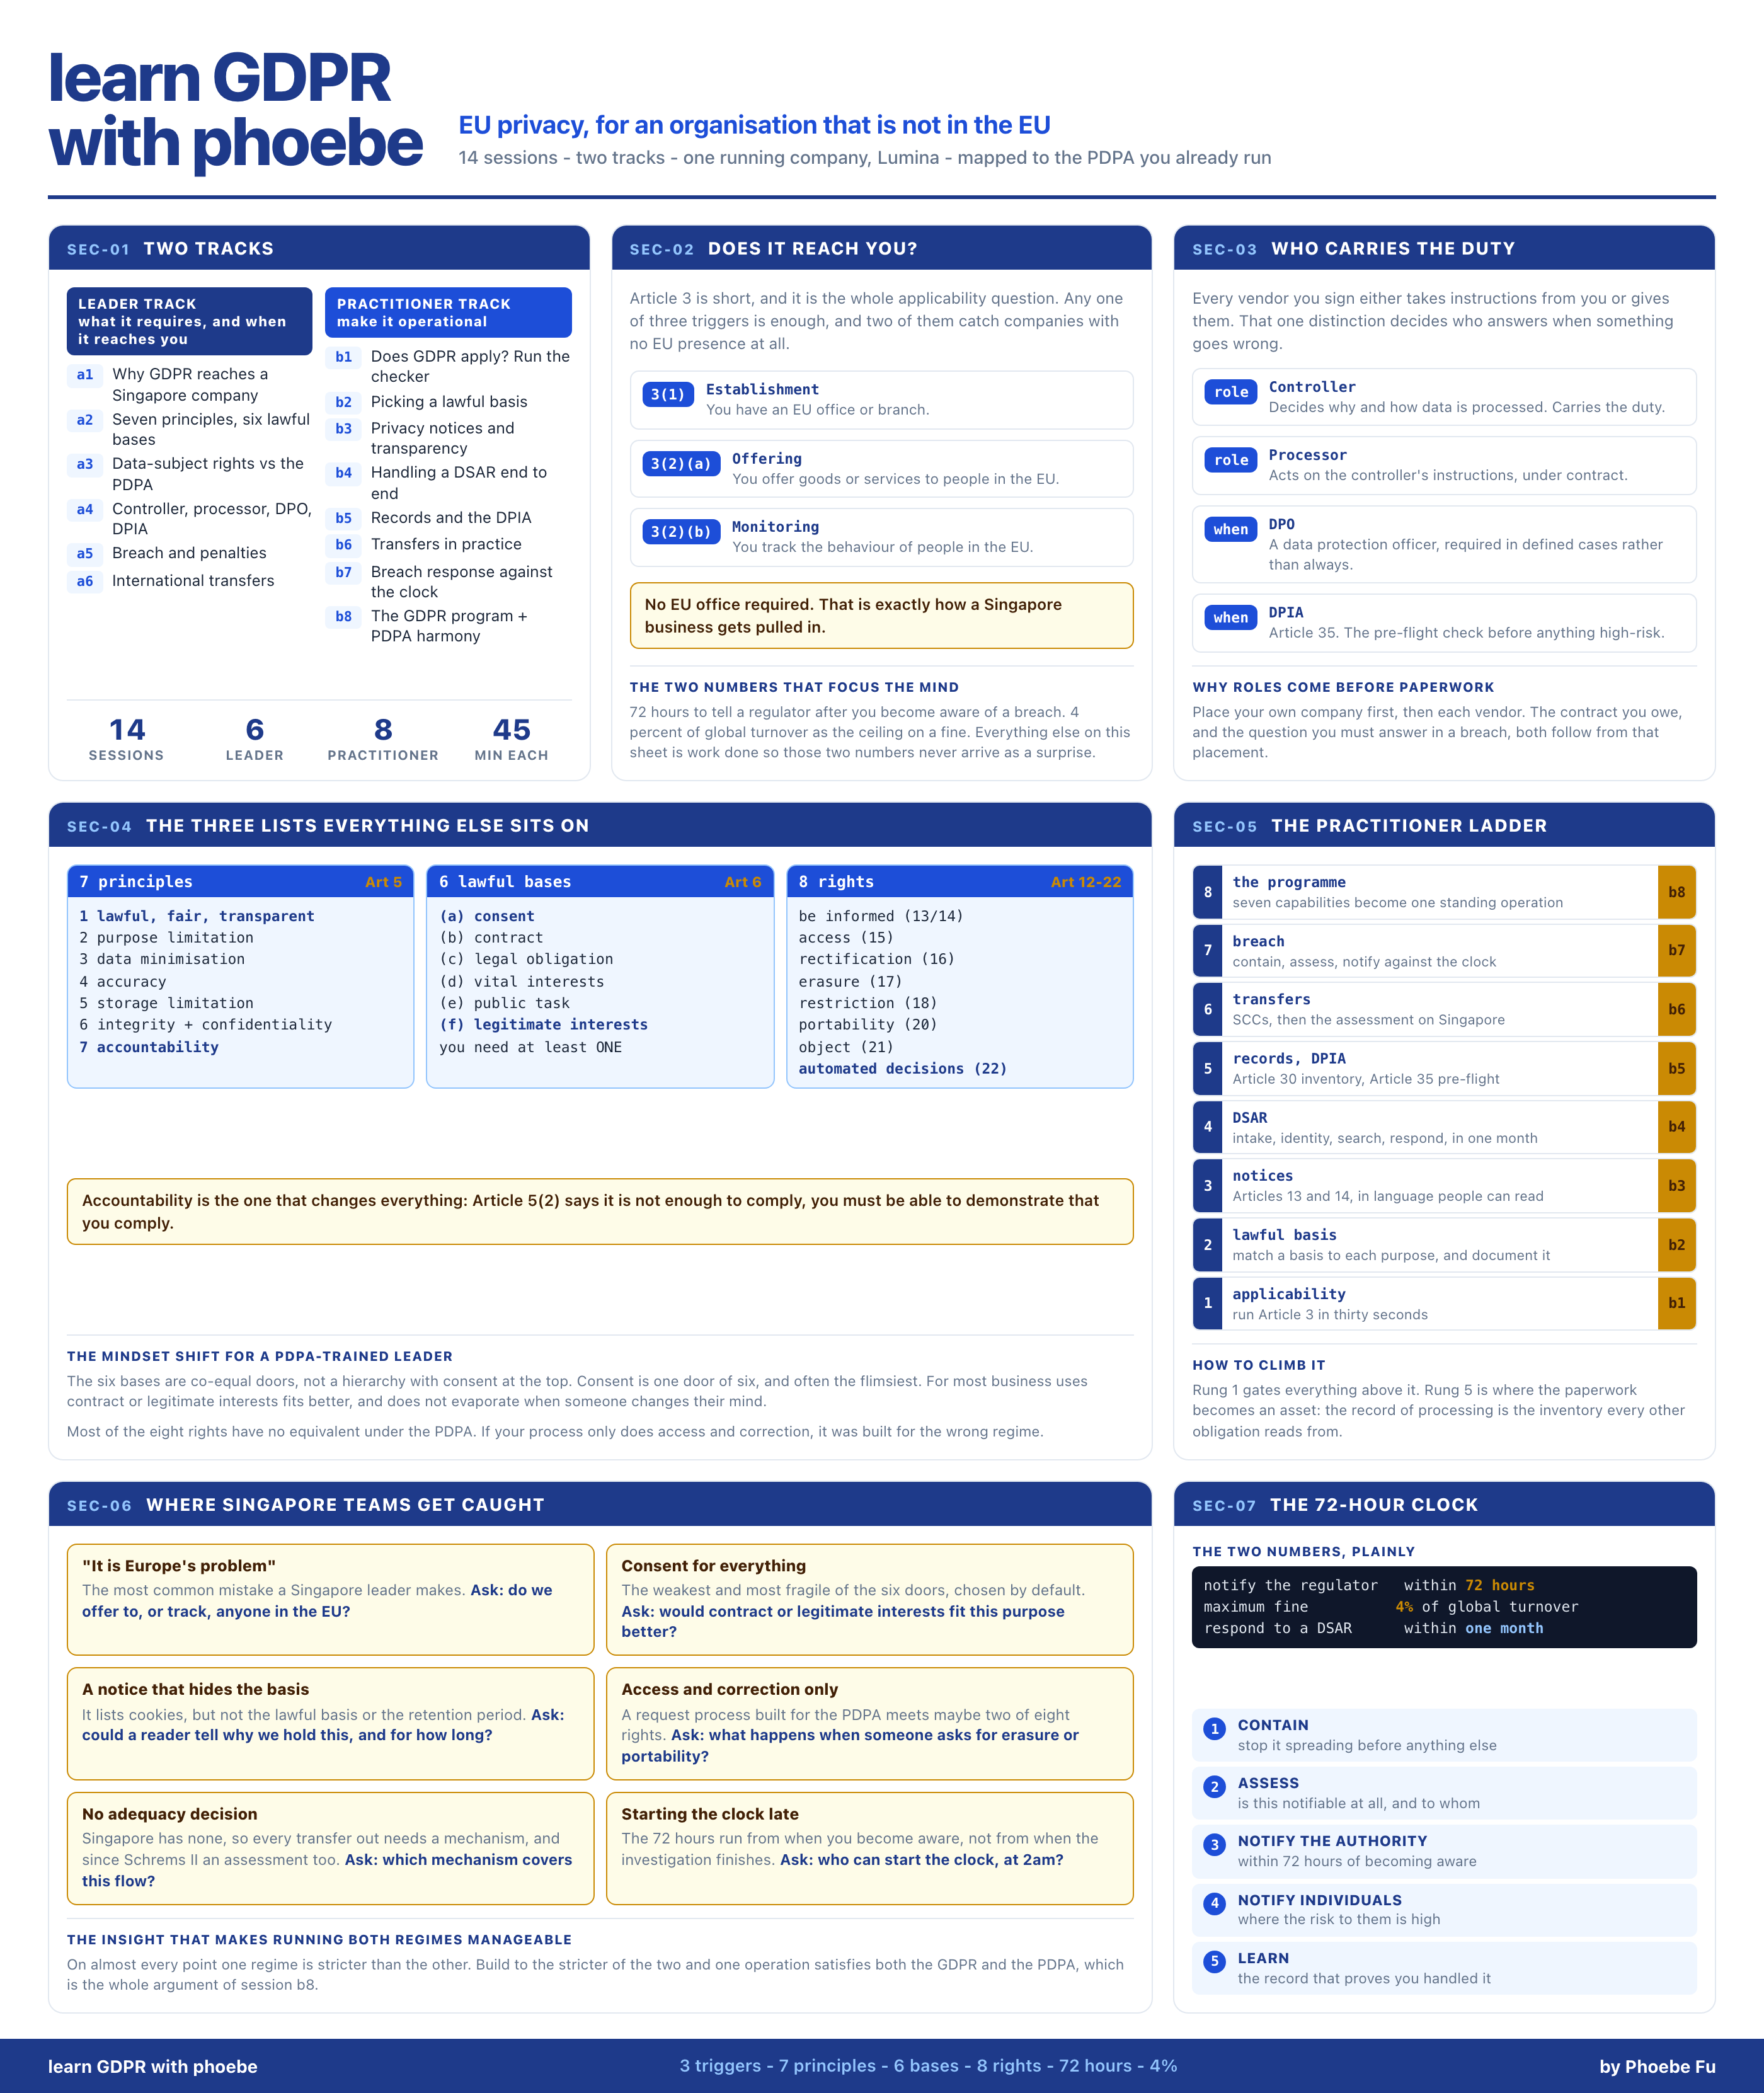
learn GDPR
with phoebe
SEC-01 TWO TRACKS
LEADER TRACK
what it requires, and when it reaches you
- a1Why GDPR reaches a Singapore company
- a2Seven principles, six lawful bases
- a3Data-subject rights vs the PDPA
- a4Controller, processor, DPO, DPIA
- a5Breach and penalties
- a6International transfers
PRACTITIONER TRACK
make it operational
- b1Does GDPR apply? Run the checker
- b2Picking a lawful basis
- b3Privacy notices and transparency
- b4Handling a DSAR end to end
- b5Records and the DPIA
- b6Transfers in practice
- b7Breach response against the clock
- b8The GDPR program + PDPA harmony
SEC-02 DOES IT REACH YOU?
72 hours to tell a regulator after you become aware of a breach. 4 percent of global turnover as the ceiling on a fine. Everything else on this sheet is work done so those two numbers never arrive as a surprise.
SEC-03 WHO CARRIES THE DUTY
Place your own company first, then each vendor. The contract you owe, and the question you must answer in a breach, both follow from that placement.
SEC-04 THE THREE LISTS EVERYTHING ELSE SITS ON
7 principlesArt 5
- 1 lawful, fair, transparent
- 2 purpose limitation
- 3 data minimisation
- 4 accuracy
- 5 storage limitation
- 6 integrity + confidentiality
- 7 accountability
6 lawful basesArt 6
- (a) consent
- (b) contract
- (c) legal obligation
- (d) vital interests
- (e) public task
- (f) legitimate interests
- you need at least ONE
8 rightsArt 12-22
- be informed (13/14)
- access (15)
- rectification (16)
- erasure (17)
- restriction (18)
- portability (20)
- object (21)
- automated decisions (22)
The six bases are co-equal doors, not a hierarchy with consent at the top. Consent is one door of six, and often the flimsiest. For most business uses contract or legitimate interests fits better, and does not evaporate when someone changes their mind.
Most of the eight rights have no equivalent under the PDPA. If your process only does access and correction, it was built for the wrong regime.
SEC-05 THE PRACTITIONER LADDER
Rung 1 gates everything above it. Rung 5 is where the paperwork becomes an asset: the record of processing is the inventory every other obligation reads from.
SEC-06 WHERE SINGAPORE TEAMS GET CAUGHT
On almost every point one regime is stricter than the other. Build to the stricter of the two and one operation satisfies both the GDPR and the PDPA, which is the whole argument of session b8.